What officers need to know.
Regulatory shifts, framework updates and operational guidance, curated for Data Protection, IT Security, Compliance and AI Governance leads. Written from the field, verified against primary sources.
UN 1965 in ADR: Liquefied gas transport between class 2.3 and § 23 GGVSEB
UN 1965 means hydrocarbon gas, liquefied, n.o.s. Anyone who loads in Germany falls under ADR Class 2 and Section 9 GGVSEB. We classify the classification, transport documents and duties of the dangerous goods officer.
Dangerous goods officer: Obligation to order, tasks and external solution according to GbV and ADR
As soon as your company transports, packs, loads or ships dangerous goods, the obligation to order in accordance with the Hazardous Goods Officer Ordinance applies. This article explains threshold values, tasks, annual reports, training, liability and the requirements for an external solution in medium-sized companies.
Safety Delegate (Sicherheitsbeauftragter): Duties and Appointment under § 22 SGB VII
Learn when and how to appoint a Safety Delegate (Sicherheitsbeauftragter) under § 22 SGB VII and manage occupational health and safety compliance.
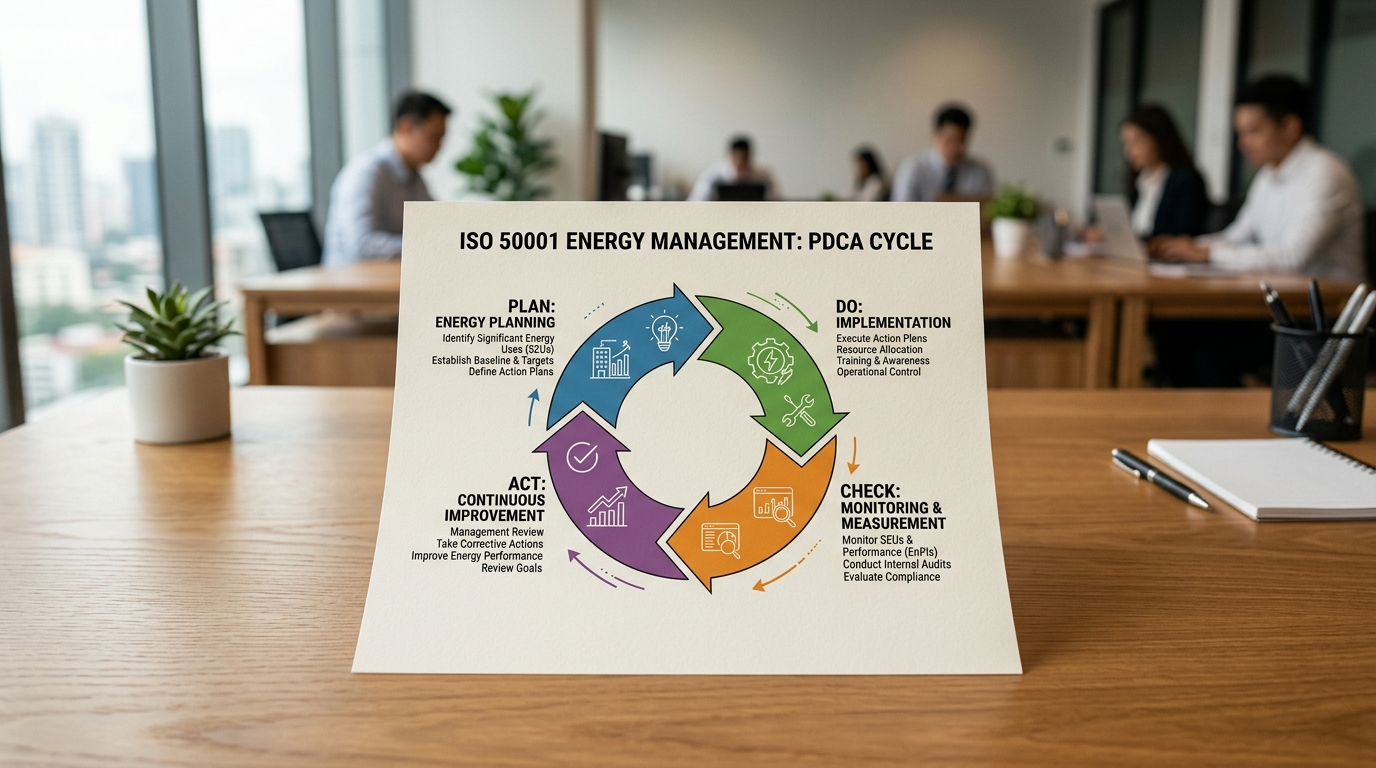
Energy Management Officer under ISO 50001 and the German EnEfG
A compliance guide for the Energy Management Officer in Germany under ISO 50001 and EnEfG, detailing thresholds, duties, liability, and software.
Transport of dangerous goods: ADR obligations, exemptions and the role of the dangerous goods officer
Anyone who transports dangerous goods or has them transported is part of a dense network of ADR, GGVSEB and GbV. This article explains classes, exemptions, shipper's obligations and the role of the dangerous goods officer.
Statement of Applicability ISO 27001: the template as an audit hinge
The Statement of Applicability is the most important template in the ISMS. Whoever maintains them passes the audit. Whoever copies them stands out in the sample contrast. This guide shows the structure, maintenance and pitfalls of the 2022 version.
BSI IT-Grundschutz vs ISO 27001: Which framework suits your organisation
Both frameworks lead to a certifiable ISMS, but solve different problems. This article systematically compares scope, depth, effort and audit logic and provides a decision-making logic for German medium-sized companies.
CSDDD Consulting: How German Mid-Market Companies Prepare for the EU Supply Chain Directive
CSDDD consulting helps companies translate the EU Corporate Sustainability Due Diligence Directive into operational supply chain processes. This article explains scope, deliverables, the relationship to LkSG, and what a credible engagement looks like.
ISO 27001 Implementation: A Practical Path Through the 2022 Revision
Implementing ISO/IEC 27001:2022 is not a documentation exercise. It is the construction of an Information Security Management System that produces evidence on demand. This article maps the implementation steps, the 93 Annex A controls, and the typical pitfalls.
ISO 27001 Consulting in Germany: Scope, 2022 Transition, NIS-2 Alignment
ISO 27001 consulting in Germany combines ISMS architecture, 93 Annex A controls and the operational reality of NIS-2, BDSG and BSI guidance. This guide outlines scope, transition timing to ISO/IEC 27001:2022, certification path and where an external information security officer fits.
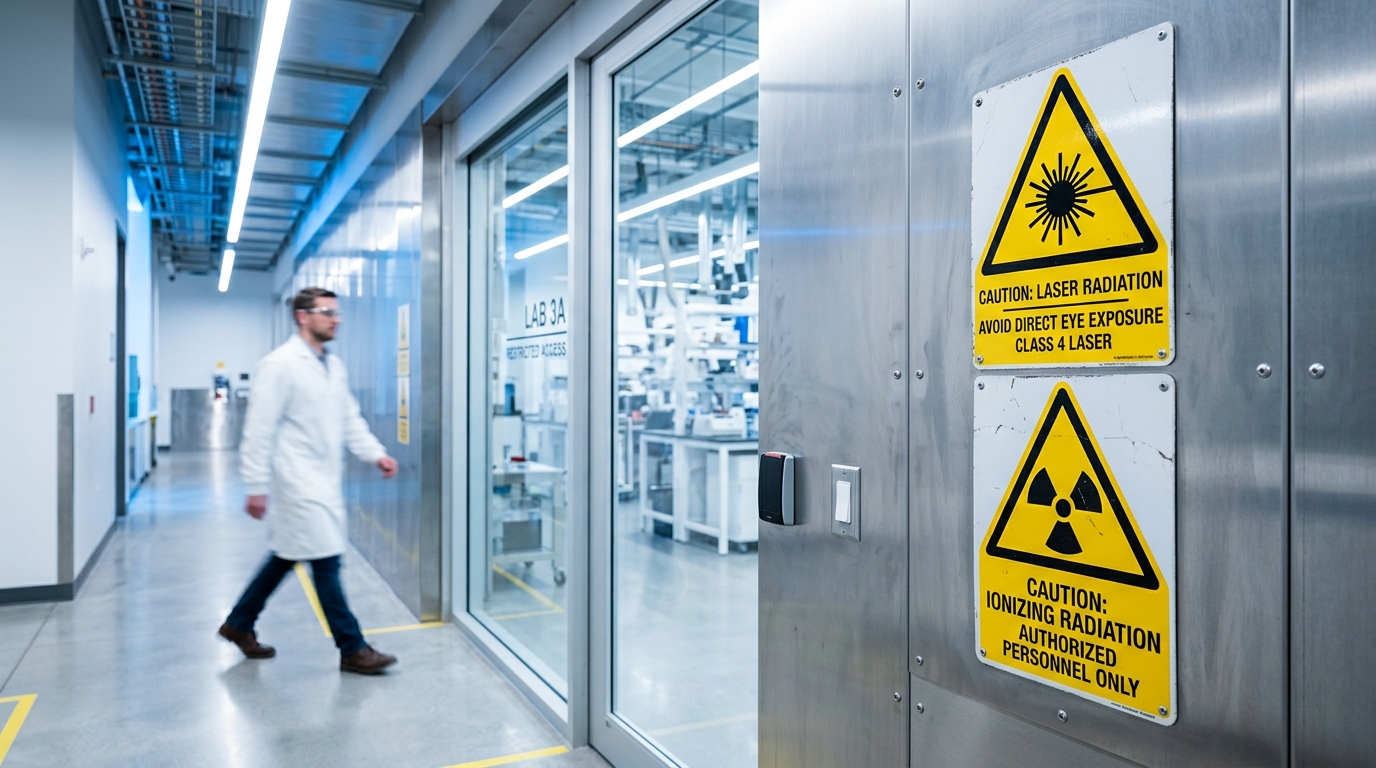
Radiation Protection: Laser Safety Officer and Nuclear Safety Officer
Learn the legal requirements, qualifications, and operational duties for Laser Safety Officers and Nuclear Safety Officers under German compliance laws.
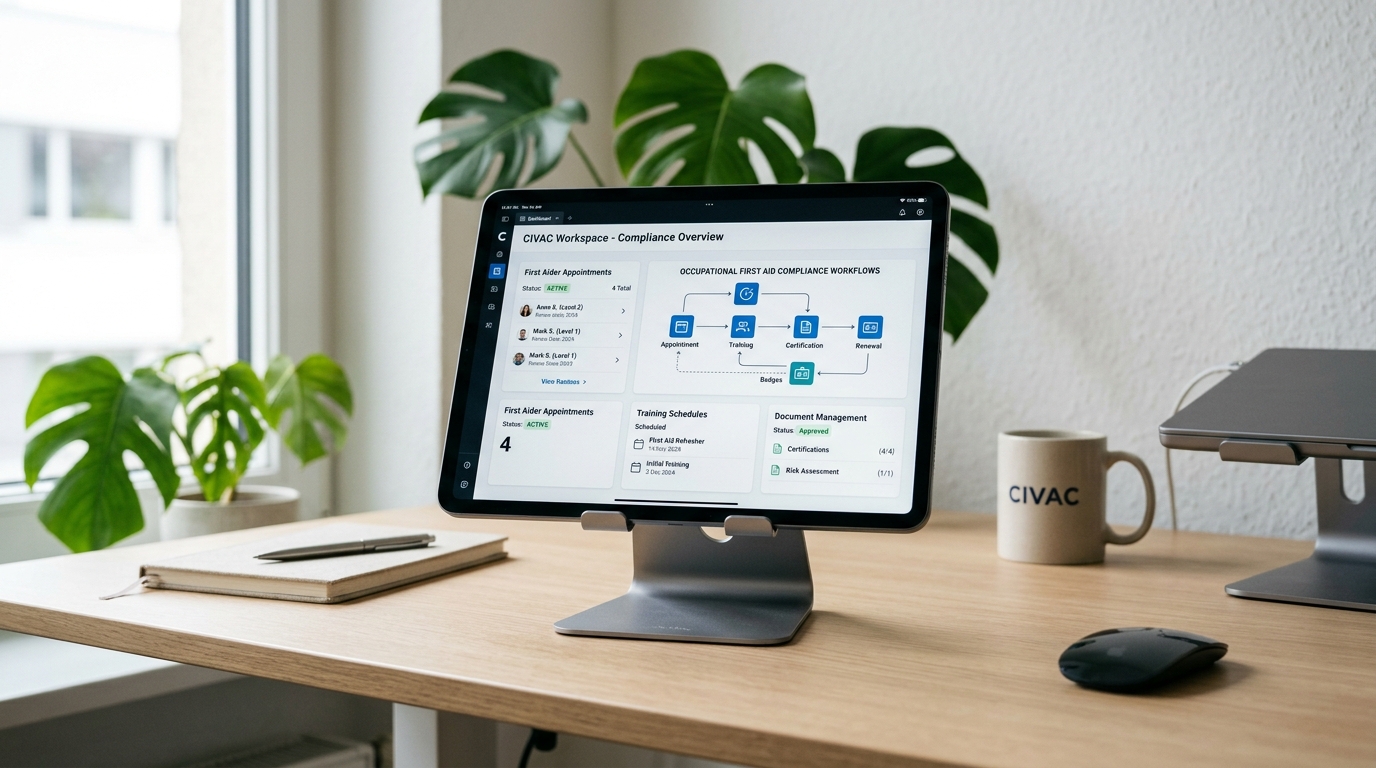
First Aid at Work: Appointing and Training First Aiders and Works Paramedics
Master Germany's workplace first aid compliance. Learn the exact headcounts, training cycles, and liabilities for first aiders and works paramedics.
DORA Regulation: What the Digital Operational Resilience Act requires of financial companies as of January 17, 2025
DORA has been directly applicable to financial companies and their ICT service providers since January 17, 2025. The article organises the five pillars, the reporting obligations, the supervision of critical third parties and the bridging to ISO/IEC 27001 along the officer tasks.
External CISO: When the virtual security officer is the right model
With NIS-2 and ISO/IEC 27001:2022, the need for strategic security leadership is growing. An external CISO takes on governance, risk and reporting lines to management without having to fill the position internally. This post explains when the model wears and when not.
DORA regulation: Obligations for banks and financial service providers since January 2025
The DORA regulation has been in effect since January 17, 2025. Banks, insurers and securities firms must manage ICT risk, incident reporting, resilience testing and third-party control according to harmonised rules. This post shows the duties in the order in which they are examined.
MSCI World ESG comparison: Which ESG variant fits which reporting requirement?
MSCI offers four ESG variants for the MSCI World alone. Anyone who only makes the comparison based on returns is overlooking the regulatory logic. This article classifies ESG Leaders, ESG Screened, SRI and Climate Paris Aligned according to CSRD, ESRS and SFDR Art. 8 / Art. 9 and shows what this means for your sustainability reporting.
ESG and EU taxonomy: Who has to report what, when and how the representative carries it out operationally
The EU taxonomy defines environmentally sustainable economic activities. The CSRD requires reporting. Who in the company provides the data points? This article organises duties, deadlines and responsibilities along the ESRS.
Animal Welfare Officer: Appointment and Duties under the German TierSchG
Learn the legal requirements for appointing an Animal Welfare Officer in Germany under TierSchG Section 10 and TierSchVersV. Avoid up to 25,000 Euro fines.
Explosion Protection and Gas Measurement: Officers and Competent Persons
A comprehensive guide to German occupational safety rules for Explosion Protection Officers and Gas Freeing Competent Persons under GefStoffV and DGUV Rules.
The best ESG funds: what they measure and what companies learn from them
Top ESG funds make decisions based on hard data, not image brochures. If a company wants to be included in MSCI ESG Leaders, FTSE4Good or S&P 500 ESG, it needs verifiable evidence according to SFDR, CSRD and ESRS.
MSCI World Small Cap ESG: Index logic, reporting obligations and consequences for German small caps
ESG indices such as the MSCI World Small Cap ESG Screened or the ESG Leaders Small Cap define which small caps can be invested in sustainable funds. Anyone who wants to remain listed as a medium-sized company or listed small cap must systematically document CSRD, EU taxonomy and controversy screening.
Vanguard Global ESG All Cap: What the ETF reveals about ESG obligations for companies
The Vanguard Global ESG Select All Cap UCITS ETF is an investment product. For listed companies and companies seeking capital, it is also an early indicator: What ESG data does the index require? Who's flying out? This article translates the methodology into concrete requirements for ESG officers, CSRD reports and audit evidence.
Classifying Deka ESG funds: What investors and compliance officers should know about the SFDR classification
Deka ESG funds are classified according to the EU Disclosure Regulation SFDR and the Taxonomy Regulation. This article explains the classification according to Articles 6, 8 and 9 SFDR, classifies PAI obligations and shows how companies manage ESG reports in an audit-proof manner.
Classify Deka ESG: What companies derive from the fund field for their own obligations
Those looking for Deka ESG are usually looking for guidance in a crowded regulatory field. This article classifies the ESG structures of large fund providers and shows what obligations this creates for companies required to report, from SFDR to CSRD to the supply chain.